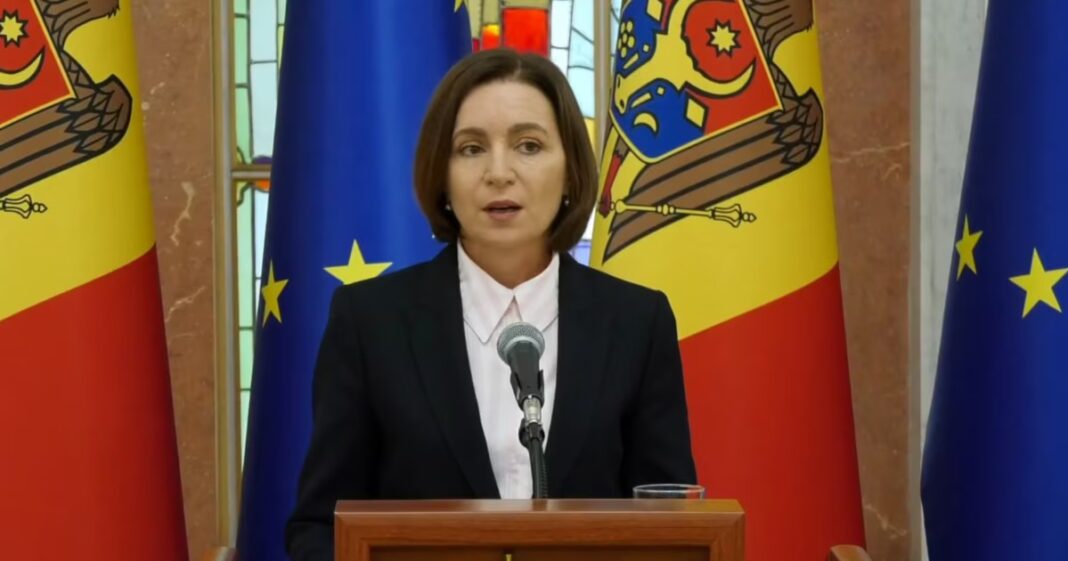

Moldova’s President Maia Sandu has convened a meeting of the Supreme Security Council following a large-scale cyberattack on government information systems. As a result of the attack, which was likely carried out using artificial intelligence, the personal data of approximately 750,000 citizens was stolen. Moldova’s population stands at nearly three million.
On 29 October, Sandu’s office announced that the meeting would take place “in the coming days”.
The day before, Prime Minister Vasile Tofan told members of the government that there were “signs of a larger-scale campaign involving foreign states”. According to him, investigators are examining “their involvement in the recent incident”. Tofan did not specify which countries might be involved.
Representatives of European countries have been warning for several months about the expansion of Russia’s hybrid operations against the backdrop of the war against Ukraine. These are hostile actions that do not amount to open warfare.
According to the Moldovan e-Government Agency (AGE), the attack affected around one million people. Attempts to steal data linked to personal identification numbers (IDNP) took place between 19 and 23 October.
The agency added that the authorities had pre-emptively suspended 82 government e-services and shut down more than 30 information systems to limit unauthorised access.
Among the data that may have been compromised are personal details: names, dates and places of birth; information on next of kin, health insurance and family doctors; details of social security payments, pensions and disability status; details of driving licences and photographs. This also includes information on vehicles and companies owned or managed by citizens, as well as financial data, including international bank account numbers (IBANs), tax arrears and payment histories. AGE reported that bank card details were not compromised and that no unauthorised changes were detected in the government registers.
It is likely that the attackers exploited vulnerabilities in services accessible without authentication and used the information obtained to attempt to steal further data.